QA and Security Built into Delivery
Review Quality and Risk
Share the product, release flow and priorities.
Quality, Security, and Compliance: One Playbook
We apply a holistic approach: test pyramid, SAST/DAST, secrets management, and least privilege. Integrated with your CI/CD, quality and security become continuous.
Flexible Engagement Models
Choose the security & QA coverage that fits your needs and budget
One-Time Audit
A review before release
A scoped review of application security, code quality and key user journeys
Monthly Retainer
Continuous protection & testing
Ongoing security monitoring, automated testing, and monthly vulnerability assessments
Full-Time Engagement
Embedded QA & Security team
Dedicated QA and security engineers working exclusively on your project
Our Testing Methodologies
We combine multiple testing approaches to check the behavior, reliability and security of your application
Unit Testing
Test individual components and functions in isolation
- Component-level validation
- Function behavior testing
- Mocking & stubbing
- Code coverage analysis
- Fast execution & CI/CD integration
Integration Testing
Verify interactions between multiple components and services
- API endpoint testing
- Database integration
- Service communication
- Third-party integrations
- Contract testing
End-to-End Testing
Test complete user workflows from start to finish
- Real user scenario simulation
- Cross-browser testing
- Mobile responsive tests
- Visual regression testing
- Performance monitoring
Manual Testing
Human-driven exploratory and edge case testing
- Exploratory testing
- Usability assessment
- Edge case discovery
- UI/UX validation
- Accessibility checks
Automated Testing
Continuous, repeatable tests running on every commit
- CI/CD pipeline integration
- Automated regression tests
- Parallel test execution
- Scheduled test runs
- Instant feedback loops
Security Testing
Identify vulnerabilities and document remediation priorities
- Penetration testing
- Vulnerability scanning
- SQL injection checks
- XSS & CSRF protection
- Evidence collection for compliance reviews
Choose the delivery model that fits.
A scoped project is the starting point. We can also support an existing team when the responsibilities and review process are clear.
| Area | Project delivery | Existing team support |
|---|---|---|
| Starting point | A defined product release or workflow | An agreed part of your existing backlog |
| Scope | Interfaces, integrations and release tasks agreed together | Named responsibilities within your team's delivery process |
| Review | Milestones, demonstrations and acceptance criteria | Reviews and progress checks with your technical owner |
| AI and automation | Approved data access, actions and user review steps | Changes within your existing architecture and permissions |
| Commercial terms | Agreed fees and milestones before work begins | Agreed capacity, responsibilities and billing |
| Handover | Source, setup notes and operating responsibilities | Documentation and knowledge transfer for your team |
What We Deliver
Test results, documented findings and prioritized remediation.
Test Automation
Unit, integration, e2e, and contract tests.
Security Hardening
OWASP, rate limiting, WAF, secrets management.
Continuous Integration
Quality gates and artifact signing.
Observability
Errors, performance, and security alerts.
Compliance & Audit
Evidence‑gathering processes for ISO/PCI/GDPR.
Chaos & Load Testing
Resilience and capacity verification.
Our Process
We validate quality and security at every step.
Discovery
Risks, scope, stakeholders.

Quality Strategy
Test pyramid, data, mocks/fixtures.
Security
SAST/DAST, secrets, IAM.
Continuous Testing
CI/CD gates and reporting.
Audit
Evidence, runbooks, playbooks.
Why Choose Skynor Labs?
End‑to‑end ownership in QA and security with measurable outcomes.
Continuous Quality
CI/CD gates, automated tests, and quality thresholds.
Strong Security
OWASP, IAM, and secrets management by default.
Observability
Early warnings for errors and performance.
Compliance
ISO/PCI/GDPR process design and evidence.
Resilience
Verified via chaos and load testing.
Transparency
Clean PR flow and transparent reporting.
Frequently Asked Questions
Case Studies
A closer look at the products and businesses we work with.
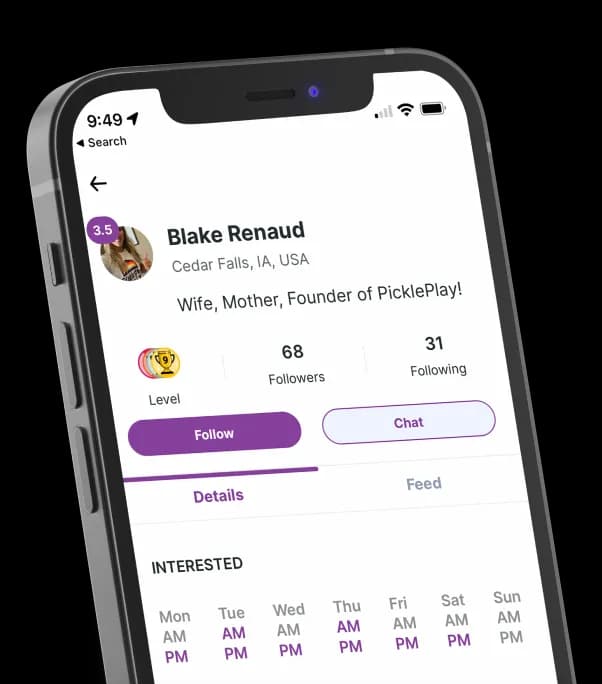
Building a Pickleball Community Platform
Developed a cross-platform product for court discovery, messaging, events and club administration across iOS, Android and the web.


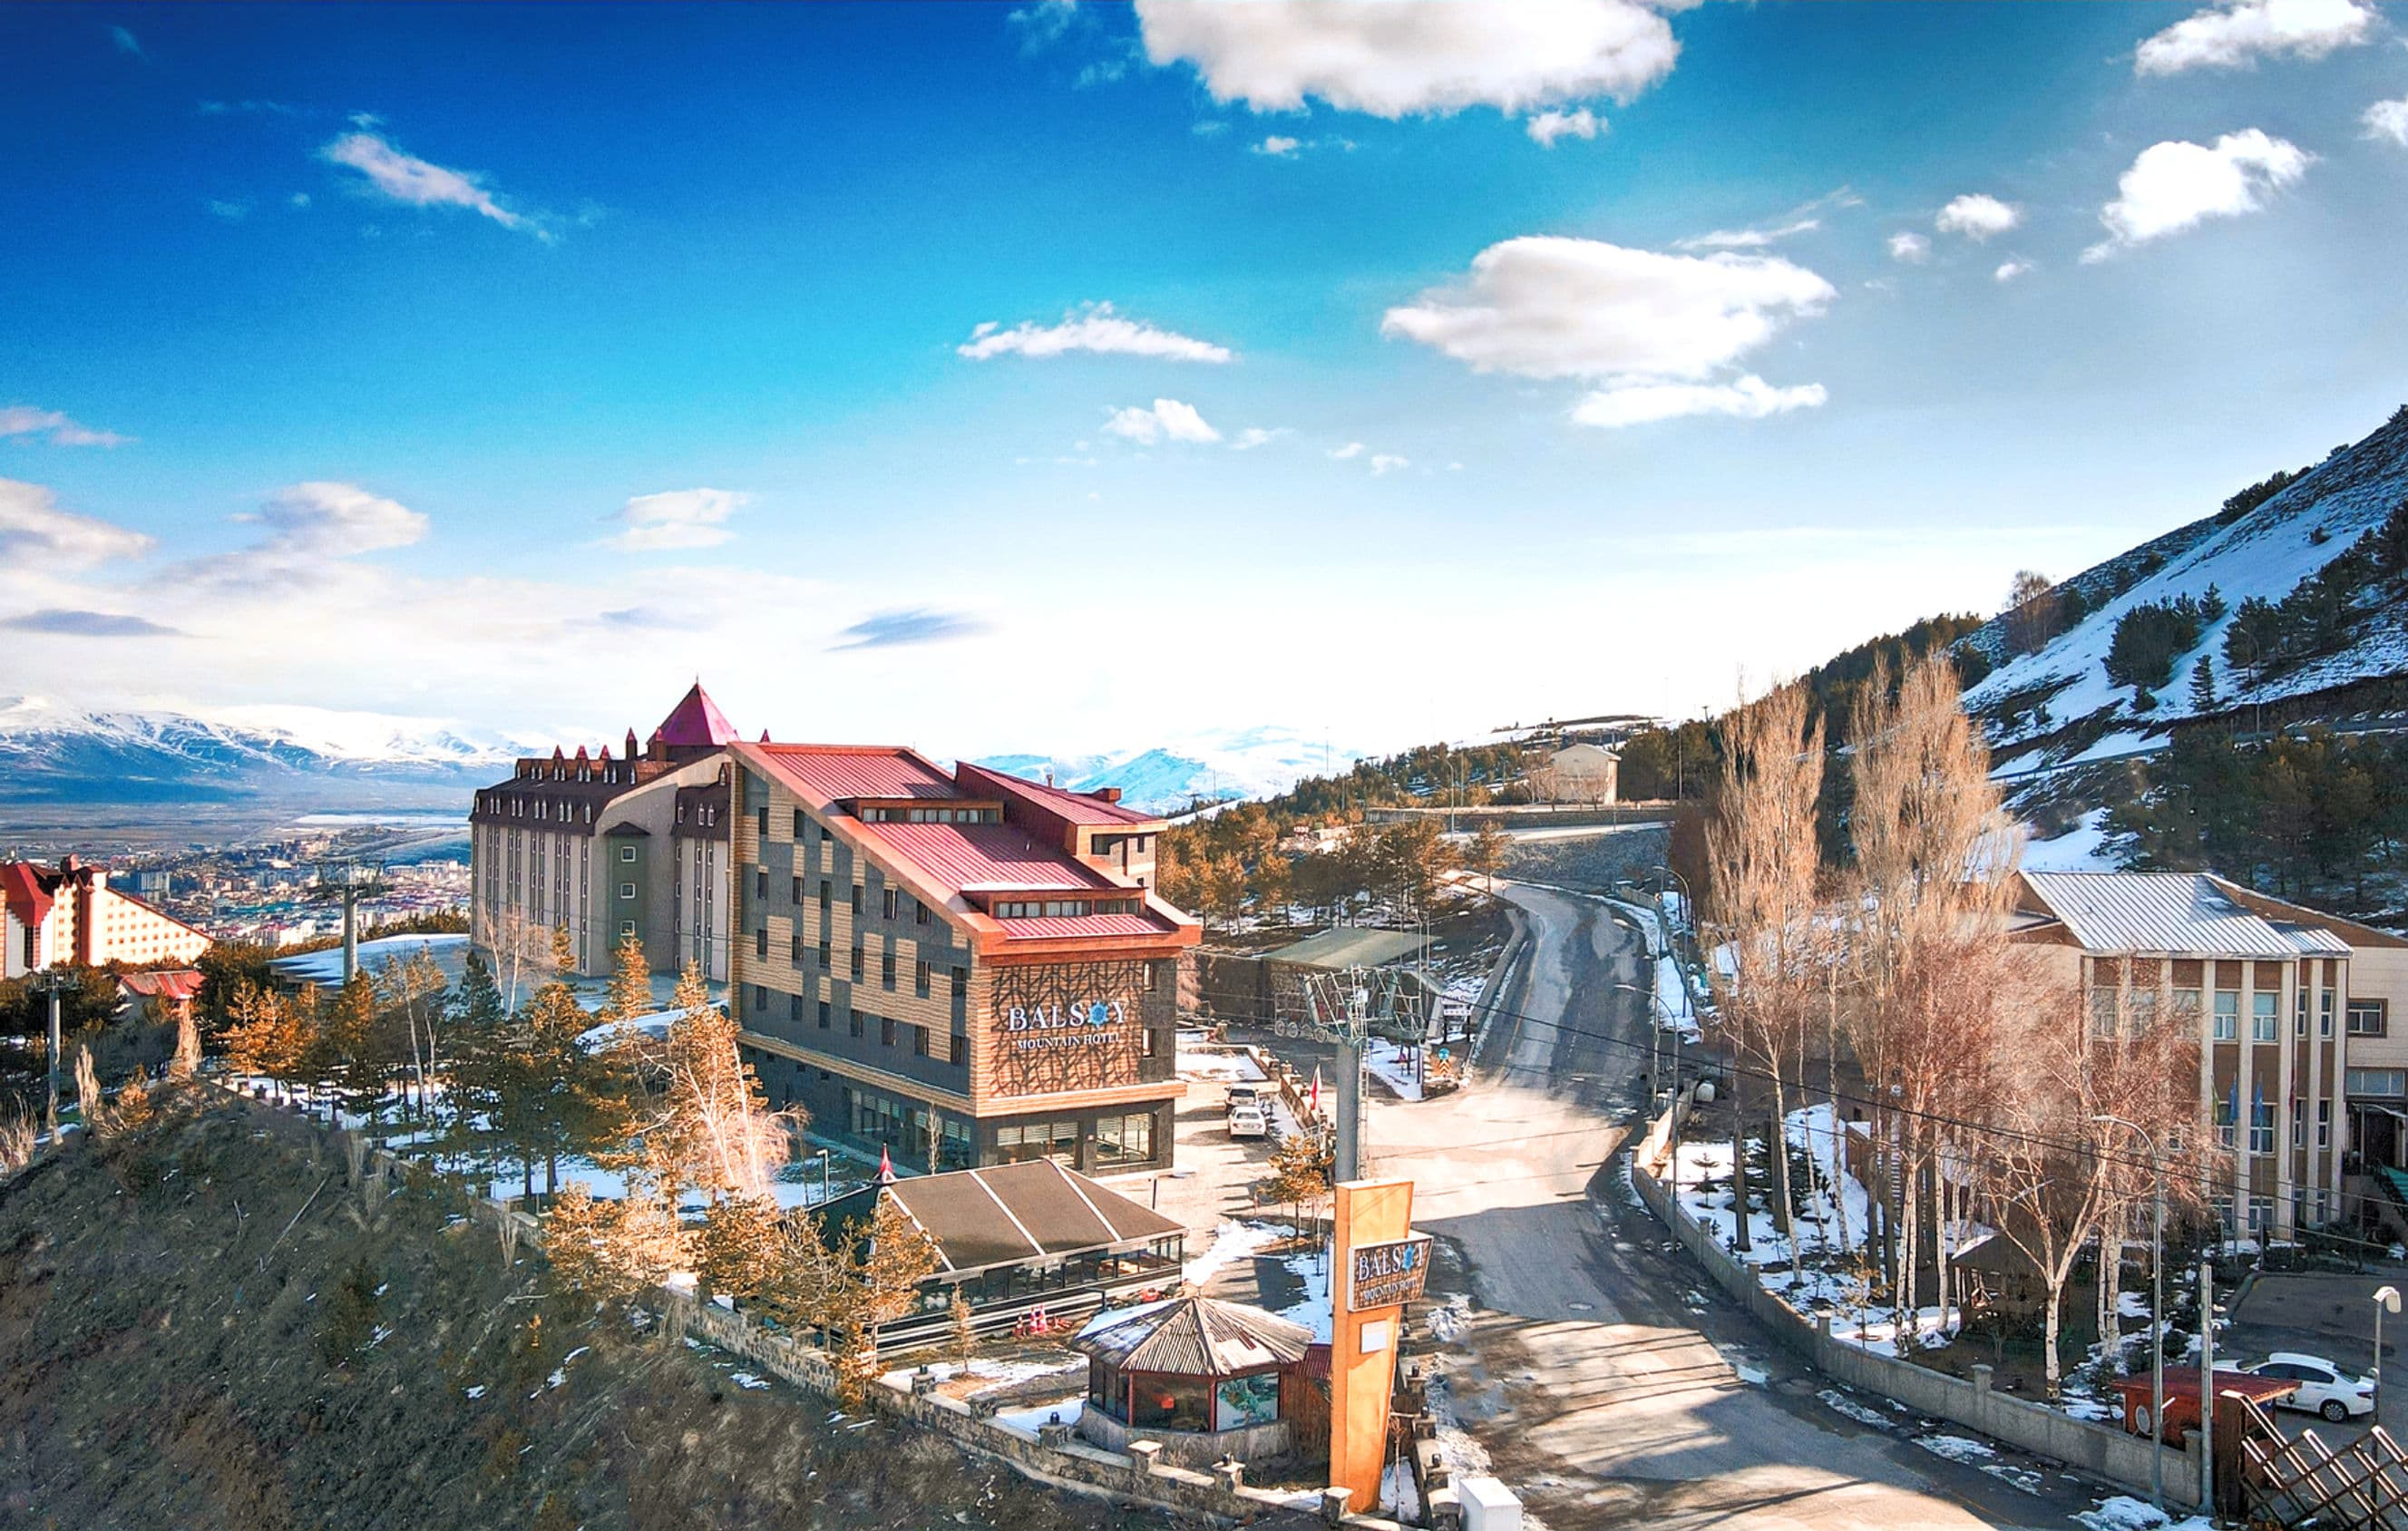
Balsoy Mountain Hotel
Google Ads, SEO, social media and brand development for Balsoy Mountain Hotel in Palandöken.
Lares Yachting
Google Ads, SEO, social media and brand development for Lares Yachting's charter business in Çeşme and Alaçatı.